

Backup/recovery and endpoint protection are considered key tools for complying with the European directive
PRAGUE, October 9, 2024 – Acronis, a global leader in cyber protection solutions, presented the results of a survey among its Czech and Slovak customers and partners regarding the implementation of the NIS 2 Directive. According to respondents' answers, only 8% of Czech organizations meet the Directive's requirements, while another 41% are working on implementation. The sectors requiring the most attention from the NIS 2 perspective include energy, healthcare, and the provision of IT solutions and services.
Stricter security requirements, mandatory incident reporting, ransomware protection, and an emphasis on supply chain security are the main building blocks of the latest Directive, creating demand for specific technical solutions. IT suppliers are seeing the greatest interest from their customers in ensuring the continuity of critical IT systems, for example with the help of Disaster Recovery technologies, as well as tools for the analysis and reporting of security incidents such as EDR or extended detection and response (XDR).
The most interesting survey findings include:
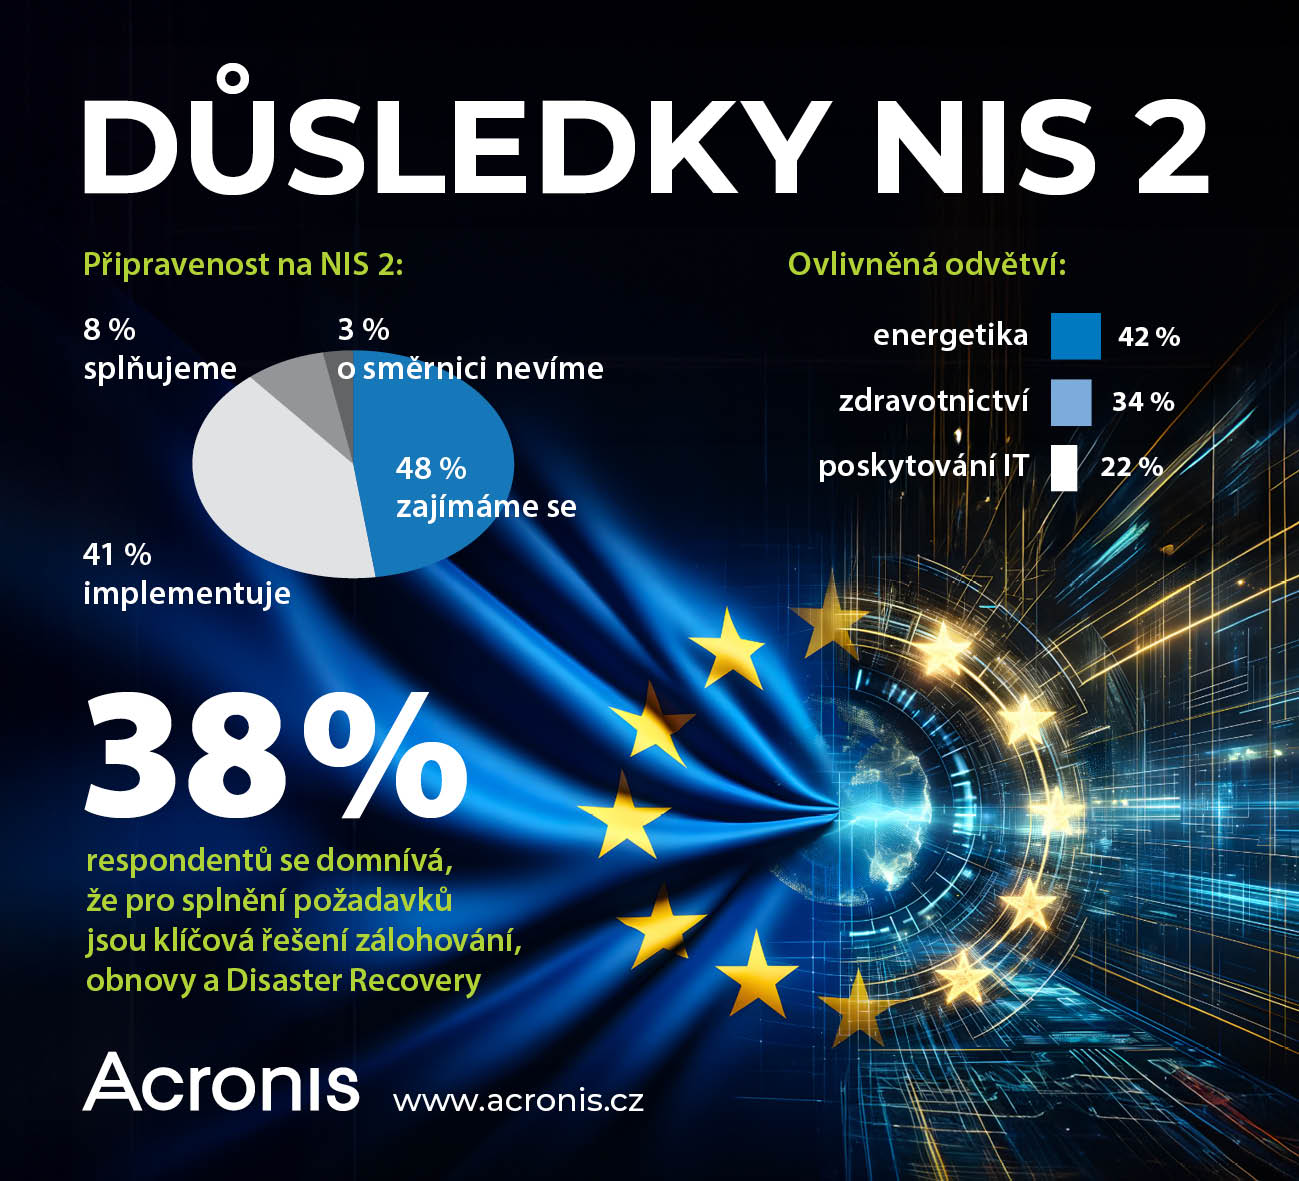
- Most respondents (48%) are only beginning to take an interest in the requirements of the NIS 2 Directive, 41% are already working on implementation, 8% already meet the requirements, and 3% claim they have not yet heard of NIS 2.
- In the opinion of those surveyed, NIS 2 will have the greatest impact on the energy sector and other network industries (42%), healthcare (34%), and the provision of IT solutions and services (22%).
- 38% of respondents believe that backup, recovery, and Disaster Recovery solutions are key to meeting the requirements, followed by EDR/XDR/MDR tools at 29% and vulnerability scanning at 27%.
“There is no doubt that the cybersecurity infrastructure of businesses and organizations must be strengthened in connection with the implementation of NIS 2,” said Štěpán Bínek, Cloud Solutions Sales Manager for Acronis at ZEBRA SYSTEMS.“For many small and medium-sized companies, this may mean a significant impact on their staffing levels and financial budgets. Therefore, in addition to building their own security capabilities, they should also consider the alternative of MSP provider services, which make it possible to meet NIS 2 requirements without the need for high initial IT investments.”
Article author: ZEBR.ai editorial team



