

In 2020, the total number of vulnerabilities increased by a further 6%
PRAGUE, March 25, 2021 – GFI Software, a provider of enterprise network security solutions, stated that businesses and organizations are increasingly threatened by combined attacks, which also exploit the growing number of identified vulnerabilities. According to statistics published in The National Vulnerability Database (NVD), 18,352 vulnerabilities emerged in 2020, representing a 6% increase compared to 2019 – the number of vulnerabilities has been continuously growing since 2017.
Small and medium-sized companies in particular neglect adequate protection across multiple areas of their infrastructure, and cyber attackers exploit this situation for combined attacks. In the primary phase, for example, a user clicks a web link in a received email, and an exploit is delivered from a risky page, vulnerabilities are exposed, and a virus infection occurs. In the secondary phase, an identified vulnerability (e.g., in a browser) and social engineering methods are used to download additional malware into the system. More attempts mean a higher probability of a successful attack.
The increasing frequency of combined attacks is the result of a number of risk factors, including:
- SMB organizations believe they are too small and insignificant for attackers to target them – on the contrary, cyber attackers go where they expect the least resistance
- Companies underestimate the fact that multiple security layers significantly reduce the risk of system compromise
- Not all identified software vulnerabilities are known to specific IT administrators
- A lax approach to patching means that, in some organizations, up to 102 days pass between the creation of a patch and its installation.
- 57% of data compromise incidents occurred as a direct result of unpatched software
“Multi-layered protection of the corporate network is now an absolute foundation of a security strategy – the only question is how many layers are needed,” said Jozef Kačala, Sales Engineer for the EMEA region at GFI Software. “If we take the aforementioned example of a combined attack, these layers definitely include vulnerability scanning and automated patch management, network perimeter protection (firewall), VPN networks, website filtering, email anti-spam, and endpoint antivirus protection.”
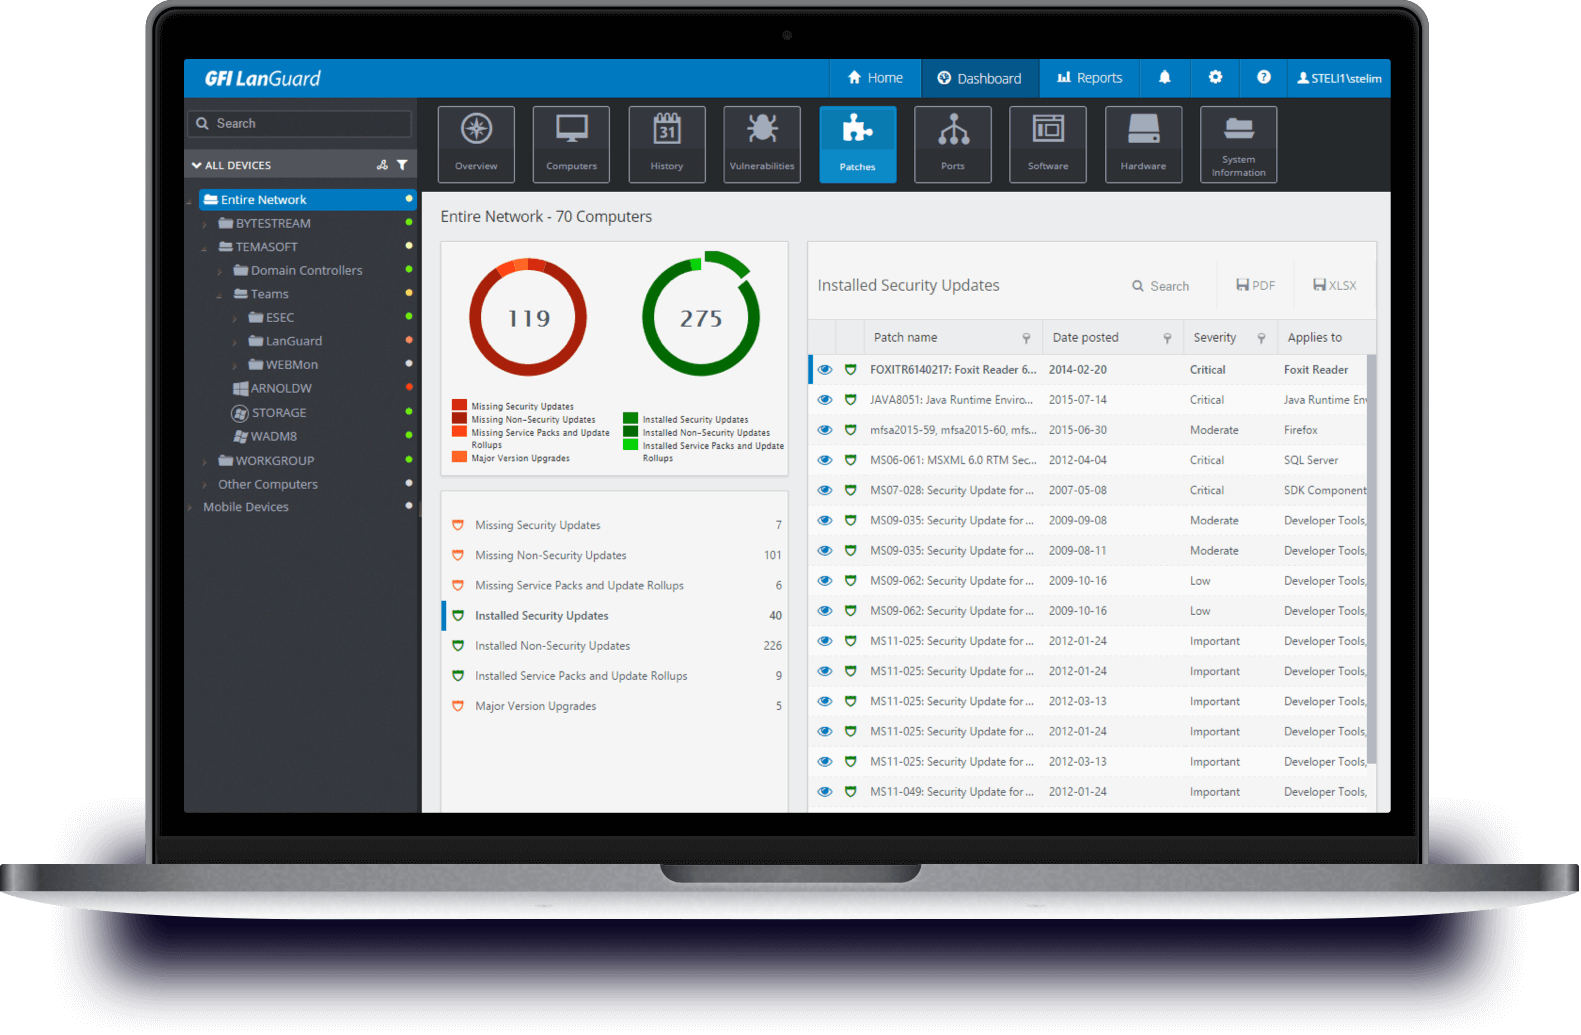
GFI Software recently introduced the Unlimited Network Security suite, which provides multi-layered IT infrastructure security through products within the GFI Unlimited model, leveraging the capabilities of GFI LanGuard, Kerio Control, and GFI MailEssentials. The suite provides protection for the network perimeter, network traffic, endpoints, and reporting on the current status of identified vulnerabilities.
Article author: ZEBR.ai editorial team



